Seven Policy Bundles and Five More Reasons Why Customers Choose ArtzAIn
When an AI agent is about to act, someone in your organization will eventually ask three questions. What was it allowed to do? Who decided? Can you show me?
Most teams can answer the first question in a slide. Very few can answer the last one with a file they can hand over. That gap is where governance programs stall, and it is the gap ArtzAIn was built to close.
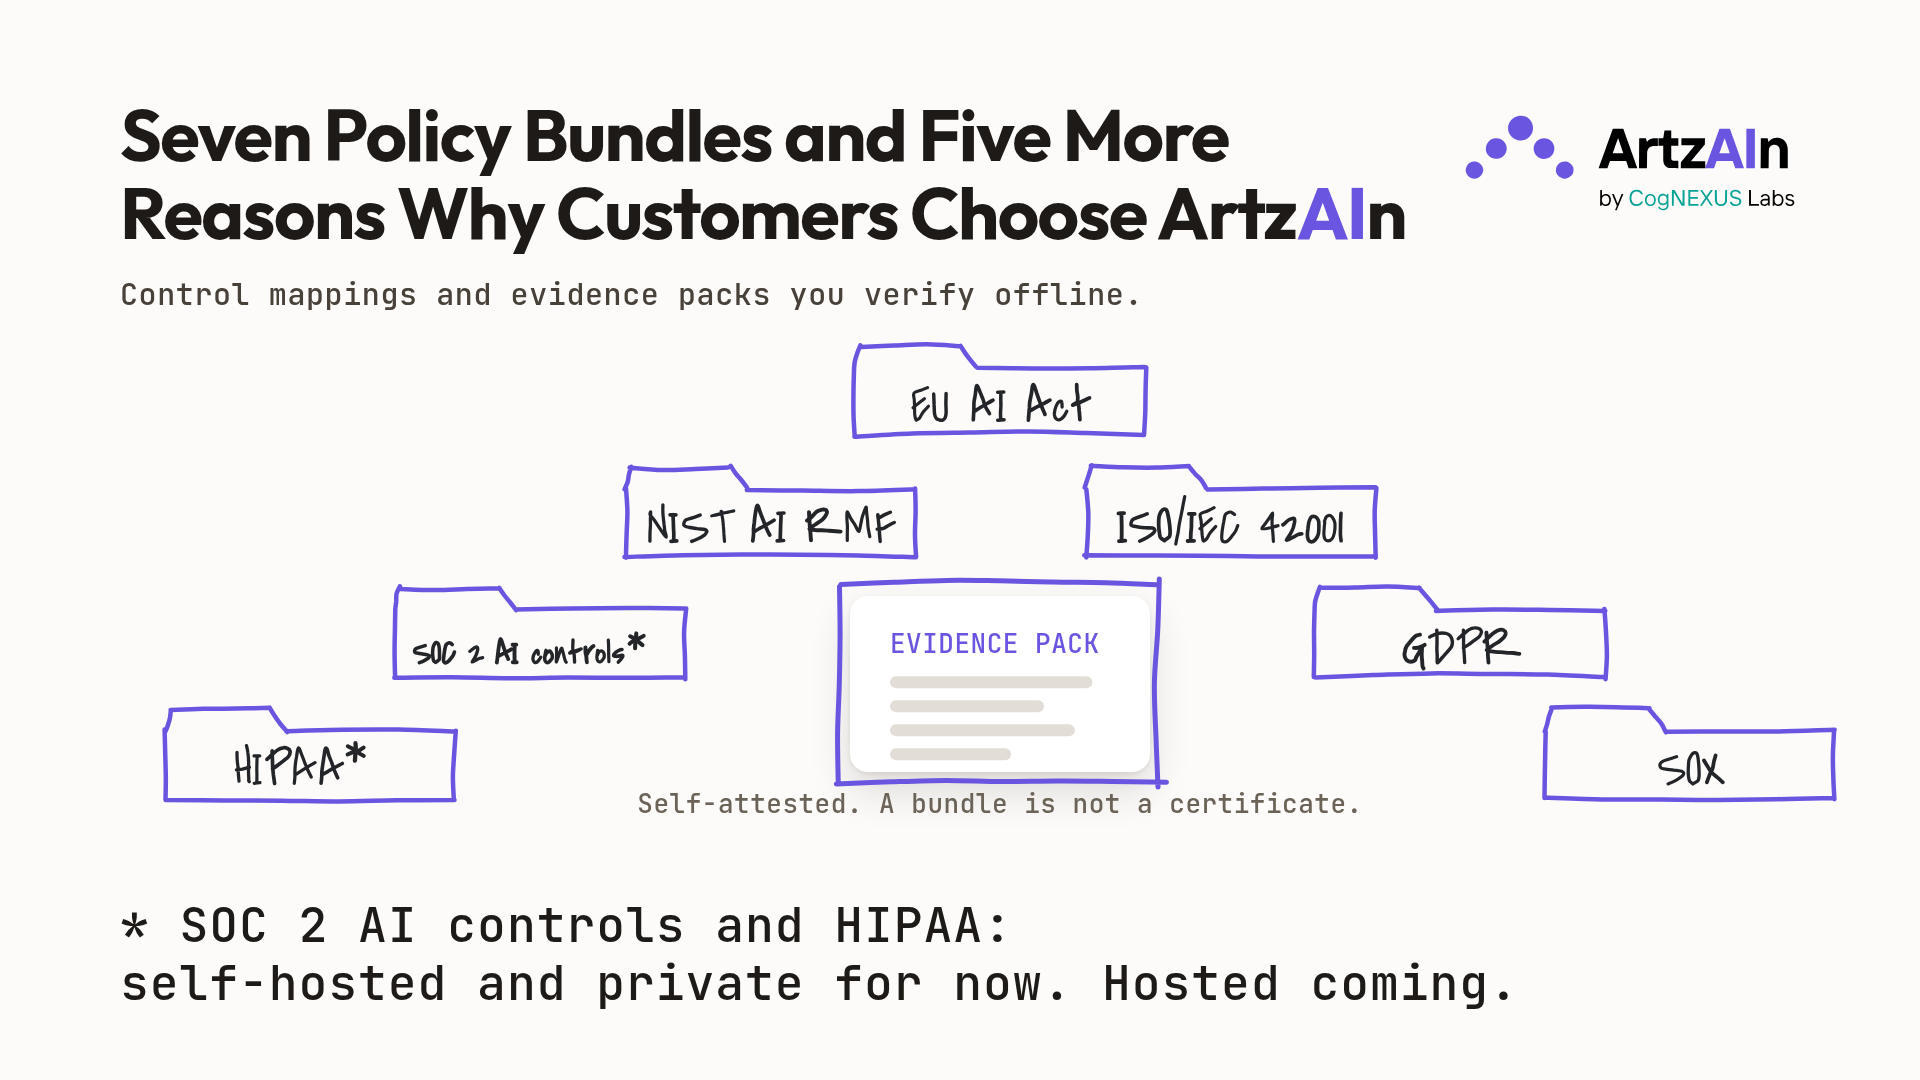
ArtzAIn now includes policy bundles for seven frameworks that Legal, Risk, and Security teams already work with:
- EU AI Act (Regulation (EU) 2024/1689)
- NIST AI Risk Management Framework
- ISO/IEC 42001
- SOC 2 AI controls
- GDPR
- HIPAA
- SOX
SOC 2 AI controls and HIPAA are available on self-hosted and private deployments for now, with hosted coming.
Each bundle comes with its control mapping and an evidence pack you can verify offline.
What a bundle is
A bundle is a starting set of policies, written against a framework, that ArtzAIn evaluates before each governed action. The control mapping shows which decisions and records relate to which parts of the framework. The evidence pack collects the signed decisions behind them so your team can review them, and so can the auditors.
A bundle is not a certificate. It is not an attestation. Evidence supports a governance program. Our exports are currently self-attested: they show what ArtzAIn decided and recorded, signed, and verifiable offline. What that evidence means for your obligations is a decision for your Legal, Risk, and Security teams.
We designed ArtzAIn to give you the controls and the records, and let your people do the work they are accountable for, faster. A lot faster.
How it fits into the path
ArtzAIn is a model-agnostic agent control plane. It works like a circuit breaker in the path of your agents. Before each governed action, your code calls a decision. Policy runs outside the model and returns allow, deny, or review. The decision is signed into the record before the answer comes back.
Add a bundle and the policies arrive with their mapping. Add your own rules next to it: internal policies, customer contracts, service levels. The bundle is a floor you build on, not a ceiling.
ArtzAIn works alongside NVIDIA OpenShell. OpenShell is the sandbox and runtime fence, and before its gateway commits a policy change, it asks ArtzAIn: allow commits, while deny, review, or no answer leaves the sandbox unchanged. ArtzAIn ships an OpenShell sidecar alongside the Python and TypeScript SDKs and the n8n, OpenClaw, and Grok Bot integrations.
What changes for the people who answer the question
For the engineer, very little. The decision call stays where it was, in front of the action. For the reviewer, risky steps arrive in the review queue for a person to decide. For the person who has to answer "can you show me," the answer becomes a file. They export the evidence pack for the period in question, verify it offline on their own machine, and share it with whoever needs to see it. Nobody has to rebuild a timeline from chat threads, and nobody has to take the vendor's word for it.
Top five reasons customers choose ArtzAIn
You can start free on your own machine with no key. We want every developer to start there. When customers tell us why they choose ArtzAIn, the same five reasons come up.
1. Receipts that outlast the question.
Questions about an agent's actions rarely arrive within a month. They arrive at the next review, the next contract renewal, or the next dispute. ArtzAIn keeps receipts, depending on plan: six months, a year, three years, or seven years by agreement, instead of a short evaluation window.
2. Evidence you hand over instead of build.
Every decision is signed and hash-chained to the one before it, so the record is tamper-evident. It verifies offline and exports as an evidence pack. Your team stops reconstructing what happened from logs and screenshots, and starts handing over a file that can be checked.
3. Permission to ship the blocked workflow.
Many agent projects stop at the same meeting, where Legal says no. Policy before the action, fail-closed behavior when the decision cannot be made, and a review path that puts a person in the loop for risky steps turn that no into a governed launch. The workflow ships with its boundaries in place.
4. One model-agnostic chokepoint.
Teams rarely run one model or one framework for long. ArtzAIn gives you one decision API across frameworks and vendors, so your controls don't need rebuilding each time the model changes. The agent registry also helps you discover agents that were never registered, so you can decide what to govern.
5. Proof that stays inside your perimeter.
Some organizations cannot send decision records outside their own walls. For design partners, we offer private deployment in your VPC, on premises, or air-gapped, with signing keys and the ledger on your own hosts. It is available on request while we work with design partners to productize it.
Where to start
You can start free on your own machine with no key. When you're ready to run it as a team, start with one policy bundle, a person in the review queue, and a record you can verify.
Peace of mind is a cleared decision with a receipt in hand.
Questions, or want to see a bundle against your own workflow? Write to hello@cognexuslabs.ai or visit https://cognexuslabs.ai/artzain.